We can't find the internet
Attempting to reconnect
Something went wrong
Hang in there while we get back on track
£85.00
It has never been this cheap. We have no record of a lower price.
£85 today · cheaper than every other day in the last 3 months
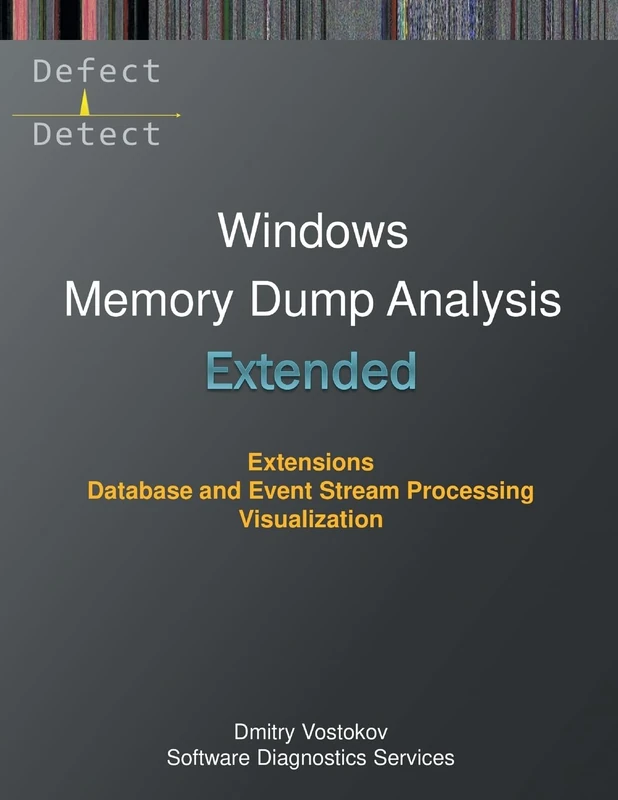
Extended Windows Memory Dump Analysis - WinDbg Extensions Guide
We'll watch every seller, every day. One email when your price arrives.
Price History & Forecast
Grey patches = out of stock. Cheaper = lower on the chart. Hover for exact prices.
Last 74 days · 74 data points (no recent data)
NEW HERE?
Amazon shows you one price. We show you all of them.
Tosheroon watches Amazon prices so you don't have to. Every product on Amazon has a price history — we make it visible. Set the price you'd actually pay, and we'll email you the second it gets there. No app, no account, one email.
WHAT'S ON THIS PAGE
when this has been cheap or pricey
where the price is heading next
all-time high & low, recent range
name your number, we'll email you
Price Distribution
Price distribution over 74 days • 1 price levels
Price Analysis
Most common price: £85 (74 days, 100.0%)
Price range: £85 - £85
Price levels: 1 different prices over 74 days
Description
Key Features
The book includes 16 hands-on exercises covering WinDbg extension development and practical memory analysis techniques.
Learn to write WinDbg extensions in C and C++ with real-world pattern mappings and extension architecture.
Connect WinDbg to NoSQL databases and streaming platforms for advanced log processing and data analysis integration.
Build on foundational pattern-oriented analysis concepts from Accelerated Windows Memory Dump Analysis courses.
Master querying and visualization techniques for WinDbg output to streamline memory diagnostics and debugging workflows.
Product Specifications
- Format
- paperback
- ASIN
- 1912636689
- Domain
- Amazon UK
- Release Date
- 28 December 2022
- Listed Since
- 03 January 2023
Barcode
No barcode data available
Similar Products You Might Like
Accelerated Linux Core Dump Analysis - GDB and WinDbg Training
The Art of Memory Forensics: Detecting Malware and Threats in Windows, Linux, and Mac Memory
Wiley
Advanced Windows Debugging
PEARSON EDUCATION
Accelerated Windows API for Software Diagnostics: With Category Theory in View (Windows Internals Supplements)
Opentask
Price unavailable
Advanced Techniques and Applications of Cybersecurity and Forensics (Emerging Technologies)
Chapman and Hall/CRC
Software Reverse Engineering: Navigating x86 Windows Applications with Ghidra
Practical Windows Forensics: Leverage the power of digital forensics for Windows systems
Packt Publishing
Fundamentals of Digital Forensics: Theory, Methods, and Real-Life Applications
Springer
A Practical Hands-on Approach to Database Forensics: 116 (Studies in Big Data, 116)
Springer
Innovations in the Memory System (Synthesis Lectures on Computer Architecture)
Springer
Python Debugging for AI, Machine Learning, and Cloud Computing: A Pattern-Oriented Approach
Apress
A Practical Hands-on Approach to Database Forensics: 116 (Studies in Big Data, 116)
Springer
Windows Malware Analysis Essentials: Master the fundamentals of malware analysis for the Windows platform and enhance your anti-malware skill set
Packt Publishing
Windows Forensics: Understand Analysis Techniques for Your Windows
Apress
Fast, Efficient and Predictable Memory Accesses: Optimization Algorithms for Memory Architecture Aware Compilation
Springer
Learning Malware Analysis: Explore the concepts, tools, and techniques to analyze and investigate Windows malware
Packt Publishing
Dynamic Memory Management for Embedded Systems
Springer
Computer and Intrusion Forensics (Artech House Computer Security Series)
Artech House
Foundations of Linux Debugging, Disassembling, and Reversing: Analyze Binary Code, Understand Stack Memory Usage, and Reconstruct C/C++ Code with Intel x64
Apress
Energy-Aware Memory Management for Embedded Multimedia Systems: A Computer-Aided Design Approach (Chapman & Hall/CRC Computer and Information Science Series)
CRC Press
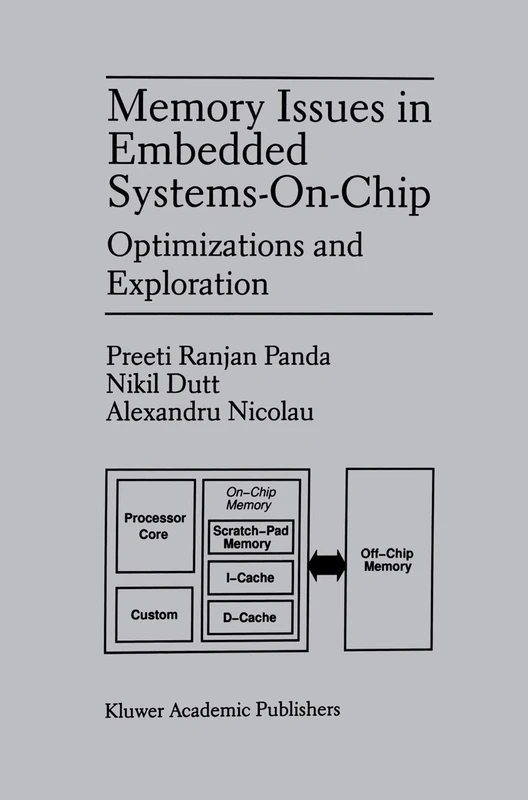
Memory Issues in Embedded Systems-on-Chip: Optimizations and Exploration
Springer
Digital Forensics Workbook: Hands-on Activities in Digital Forensics
CREATESPACE
Windows Forensic Analysis Toolkit: Advanced Analysis Techniques for Windows 8
Elsevier
Windows Registry Forensics: Advanced Digital Forensic Analysis of the Windows Registry
Syngress